
For most people, the safest way to send large files securely is a cloud storage link with a password and a short expiration window. If the recipient needs speed and no server storage in between, a serverless peer-to-peer transfer works too. Teams under compliance rules should use managed transfer or SFTP instead. The right pick depends on file size, recipient setup, and how much of an audit trail you need.
TL;DR:
- Sending large files via cloud links remains safest for most users, provided links are password-protected and set to expire quickly.
- Peer-to-peer transfer tools are ideal for large files sent to trusted recipients when privacy is priority, but require both parties to be online simultaneously.
- Managed transfer or SFTP platforms are necessary for teams needing audit logs, compliance, and automated retention policies.
- Proper security practices include encrypting files individually, using separate channels for links and passwords, and deleting shared links after receipt confirmation.
- For sensitive data, always verify recipient identity, use end-to-end encryption, and remove metadata or unnecessary details from files before sending.
Table of Contents
- Secure Methods to Send Large Files: A Quick Comparison
- How Do You Choose the Right Transfer Method?
- Step-by-Step: Sending a Large File With a Secure Cloud Link
- When Peer-to-Peer Transfer Makes Sense (and When It Doesn't)
- SFTP and Managed Transfer for Teams That Need an Audit Trail
- Security Practices That Actually Reduce Your Risk
- Fixing Slow or Failed Transfers
- Legal and Compliance Considerations for Large File Transfers
- Assessing and Reducing the Real Risks in Large File Transfers
- Verifying Recipient Identity Before You Hit Send
- Which File Formats and Prep Steps Protect Sensitive Data
- Encryption Standards: What's Actually Protecting Your File
- An Operational Checklist for Teams That Move Large Files Often
- Send Files Securely Without Building Infrastructure
- Sources
Secure Methods to Send Large Files: A Quick Comparison
Every method trades something for something else. Here's what each one actually gets you.
- Cloud share links (Google Drive, Dropbox, OneDrive): Upload once, share a link. Best for recipients with no special software, and Microsoft recommends this over email attachments for exactly that reason. The tradeoff: files sit on someone else's server until you delete them, so encryption and access settings matter.
- Dedicated transfer services: Built specifically for one-time large sends, often with automatic expiration. Free tiers usually have caps in the low single-digit gigabytes range.
- Peer-to-peer/serverless streaming: Moves data directly device to device with nothing stored on a middleman server. Great for privacy, but both sides need to stay online simultaneously.
- SFTP, FTPS, and managed file transfer: The professional tier. Logging, retention rules, and access controls built in, at the cost of setup complexity.
- Physical shipment: An encrypted external drive mailed overnight. Slow, but immune to network failure and bandwidth caps entirely.
A single 100GB video file going to one trusted colleague fits a peer-to-peer tool well. A law firm sending client documents weekly needs the audit trail that managed transfer provides.
How Do You Choose the Right Transfer Method?
Run through these five checks before picking a tool:
- File size versus your upload speed. A large file on a modest connection can take several hours to upload. Know that number before you promise a deadline.
- What the recipient can actually receive. Corporate firewalls block unfamiliar domains, and some email clients still choke on attachments over 25MB, per guidance on attachment size limits.
- How sensitive the content is. Client contracts and medical records need end-to-end encryption and an audit log. Vacation photos don't.
- Whether you need the file to persist or disappear. A stored backup costs more in storage fees; a transient link costs nothing once it expires.
- How reliable your connection is. If your upload drops mid-transfer, does the tool resume where it left off, or does it start over?
Pro Tip: Before choosing a service, send yourself a 1GB test file first. It exposes firewall blocks and slow upload ceilings before they wreck a real deadline.
Step-by-Step: Sending a Large File With a Secure Cloud Link
Here's the actual workflow, not the marketing version of it.
- Compute a checksum before you upload anything. Run the file through a SHA-256 generator and save the hash somewhere separate from the file itself.
- Compress if it helps. Zipping a folder of documents or images can shrink transfer time noticeably; it won't do much for already-compressed video.
- Upload and configure security settings: set a password, pick an expiration in a short range typically used for business purposes, and enable one-time download if the tool supports it.
- Send the recipient the link and the password separately. Text the password, email the link. Never put both in the same message.
- Confirm the download, then have the recipient re-run the checksum. Matching hashes mean the file arrived intact.
If the transfer fails partway:
- Check whether the tool supports resume from the last byte before restarting.
- Try a different network (mobile hotspot instead of office Wi-Fi) if a firewall is the suspected culprit.
- Fall back to a peer-to-peer service if the recipient's storage quota is the bottleneck.
When Peer-to-Peer Transfer Makes Sense (and When It Doesn't)
Serverless transfer tools stream your file directly to the recipient's device using a direct connection, often built on WebRTC. Nothing touches a third-party server in between, which is why these services can offer no-size-limit transfers that would be impossible if they had to warehouse the data themselves.
The catch: both people have to be online at the same time, with the sender's browser tab open until the transfer finishes. Close the tab, lose the connection, and you start over.
- Good fit: one enormous file, a recipient you trust, and no need for a paper trail afterward.
- Bad fit: sending to a corporate recipient behind a strict firewall, or any situation where you need proof of who downloaded what and when.
Pro Tip: *Keep a P2P tool bookmarked as your backup option.
SFTP and Managed Transfer for Teams That Need an Audit Trail
Browser-based tools are built for one-off sends. SFTP, FTPS, and managed file-transfer platforms are built for repetition and oversight, which is why regulated industries lean on them.
- Audit logs that record exactly who accessed a file and when, not just that a link was clicked.
- Granular permissions so different team members get different access levels on the same transfer folder.
- Retention policies that automatically delete files after a set period instead of leaving them live indefinitely.
- Integration options for pushing files directly from internal systems without a human copying anything by hand.
The tradeoff is setup time. Someone has to configure the server, manage credentials, and maintain it. Choose managed transfer when your team sends large files weekly, not once a quarter, or when a compliance officer will eventually ask for proof of access.
Security Practices That Actually Reduce Your Risk
Most large-file leaks trace back to skipped basics, not sophisticated attacks. Cover these every time:
- Use a tool with end-to-end or client-side encryption, meaning the provider itself can't read your file contents, a standard several dedicated encryption platforms build their entire product around.
- Set a password on every share link and keep expirations short, ideally under a week for anything sensitive.
- Turn on multi-factor authentication for your storage account, not just the file link.
- Use one-time download links when the option exists so a forwarded link can't be reused indefinitely.
- Strip sensitive details out of filenames. "Q3_Layoffs_Draft.xlsx" tells anyone who sees the link preview more than it should.
- Delete or deactivate the share once the recipient confirms receipt. A live link sitting forgotten for months is a liability with no upside.
Pro Tip: Set a recurring calendar reminder to audit active share links monthly. Most people forget links exist long after the transfer is done.
Fixing Slow or Failed Transfers
- Use a service with resume support, and tell your recipient how to trigger it if their download stalls partway.
- Split large folders into smaller zipped batches when a single massive file keeps timing out. You lose the clean folder structure, but you gain reliability.
- Schedule big uploads overnight or use a bandwidth-limiting setting so the transfer doesn't choke your video calls.
- If a transfer repeatedly fails, check your firewall and antivirus settings before blaming the service. Both commonly interrupt long-running uploads.
Legal and Compliance Considerations for Large File Transfers
Rules vary sharply by industry and by where your recipient is located, and ignorance doesn't count as a defense.
Under the EU's General Data Protection Regulation, personal data transferred outside the European Economic Area needs an approved safeguard, such as standard contractual clauses, and the sender remains accountable for how that data is protected in transit. Sending personal data through an unencrypted link that stores data outside the EEA can trigger exposure under GDPR, regardless of intent.
In the United States, HIPAA requires covered entities to protect electronic protected health information both at rest and in transit, which rules out unencrypted email attachments or public links with no password for anything containing patient data. A file-sharing tool doesn't need to say "HIPAA compliant" on its homepage to be usable this way, but it does need encryption, access logging, and the ability to execute a business associate agreement if you're a healthcare provider or handle health data on one's behalf.
Financial services face their own layer, often requiring specific retention periods and audit trails under regulations that vary by country and by financial product type. The common thread across every regulation: encryption alone doesn't satisfy compliance. You also need documented access control, a retention or deletion policy, and proof of who touched the file. Before sending anything regulated, check your organization's specific obligations rather than assuming a "secure" label on a transfer tool covers you automatically.
Assessing and Reducing the Real Risks in Large File Transfers
The biggest risk in most large-file transfers isn't a hacker intercepting your upload mid-flight. It's a link forwarded to the wrong person, a password sent in the same message as the file, or a share left active for months after anyone needed it.
Start by categorizing what you're sending. A marketing video and a client's tax return carry wildly different consequences if exposed, and your transfer method should scale with that difference. For low-sensitivity files, a basic cloud link is fine. For anything containing personal, financial, or health data, encryption and access logging stop being optional.
Second, map who could realistically access the file at each step: your device, the transfer service's servers, the network in between, and the recipient's device. A weak link anywhere in that chain undermines the whole transfer, no matter how strong the encryption is elsewhere.
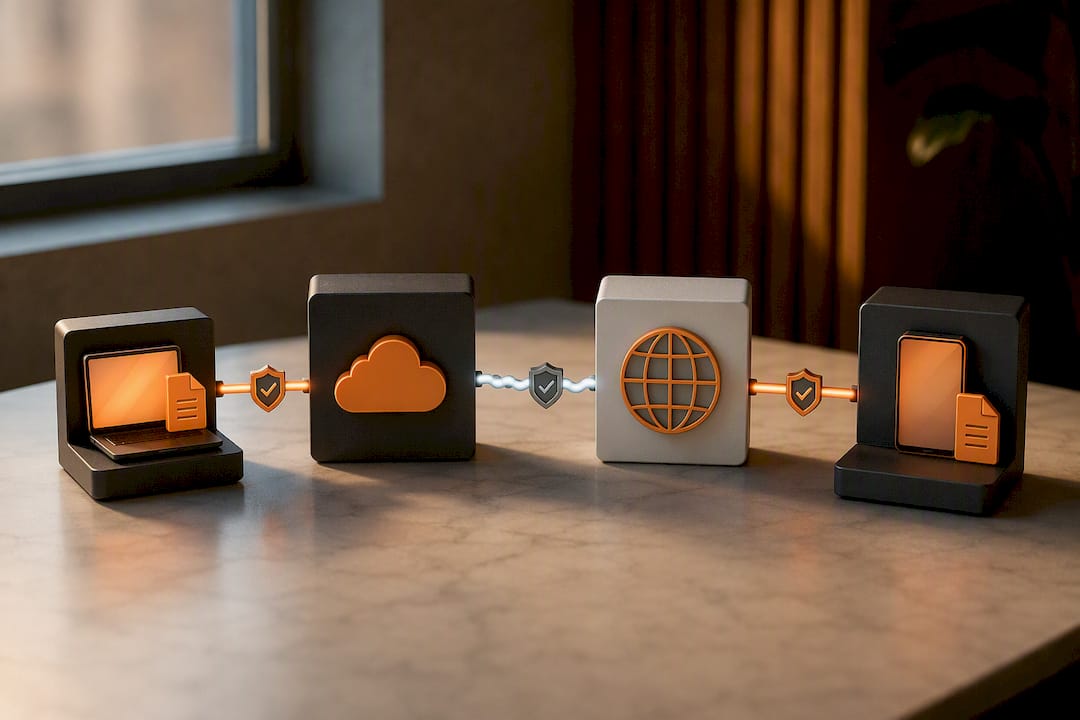
Third, build in expiration by default rather than by memory. Set every share link to expire automatically instead of relying on yourself to remember to delete it later. Combine that with one-time download links where available, since a link that self-destructs after one use can't be quietly reshared weeks later.
Finally, treat large attachments as a bigger liability than small ones. A 200MB contract mistakenly sent to the wrong email address is bad. A 20GB archive of client files sent the same way multiplies the damage by every document inside it. Slow down specifically when the file is big.
Verifying Recipient Identity Before You Hit Send
A password-protected link is only as secure as the channel you use to share the password. Sending both the link and the password through the same email thread defeats the purpose entirely, since anyone who intercepts one message gets both pieces.
Split your channels. Send the file link through email and the password through text message or a phone call. For high-stakes transfers, like legal settlements or wire-related documents, verify the recipient's identity through a method they can't fake over email, such as a callback to a known phone number.
Business email compromise attacks frequently target exactly this workflow, impersonating a known contact to redirect a file transfer or request a password reset. If a request for a large file transfer arrives with unusual urgency or a slightly altered email address, confirm through a separate channel before sending anything.
For team environments, tie file access to your organization's existing identity system rather than creating one-off logins. Multi-factor authentication on the sending account matters just as much as encryption on the file itself, since a compromised account with no MFA lets an attacker bypass every other security setting you configured.
Some managed transfer platforms support single sign-on integration, letting you extend your company's existing authentication rules to file shares instead of managing separate credentials for every transfer.
Which File Formats and Prep Steps Protect Sensitive Data
Before a sensitive file leaves your machine, its format matters almost as much as the transfer method carrying it.
Encrypt the file itself, not just the transfer channel, when the content is highly sensitive. A password-protected ZIP or an encrypted PDF stays protected even if the transfer link itself is somehow compromised or forwarded to the wrong person. Tools like 7-Zip and built-in PDF password protection handle this without extra software.
Strip metadata before sending. Documents, images, and PDFs often carry hidden author names, GPS coordinates, or edit histories that reveal more than the visible content does. Most office suites include a "remove personal information" or "inspect document" option that clears this before export.
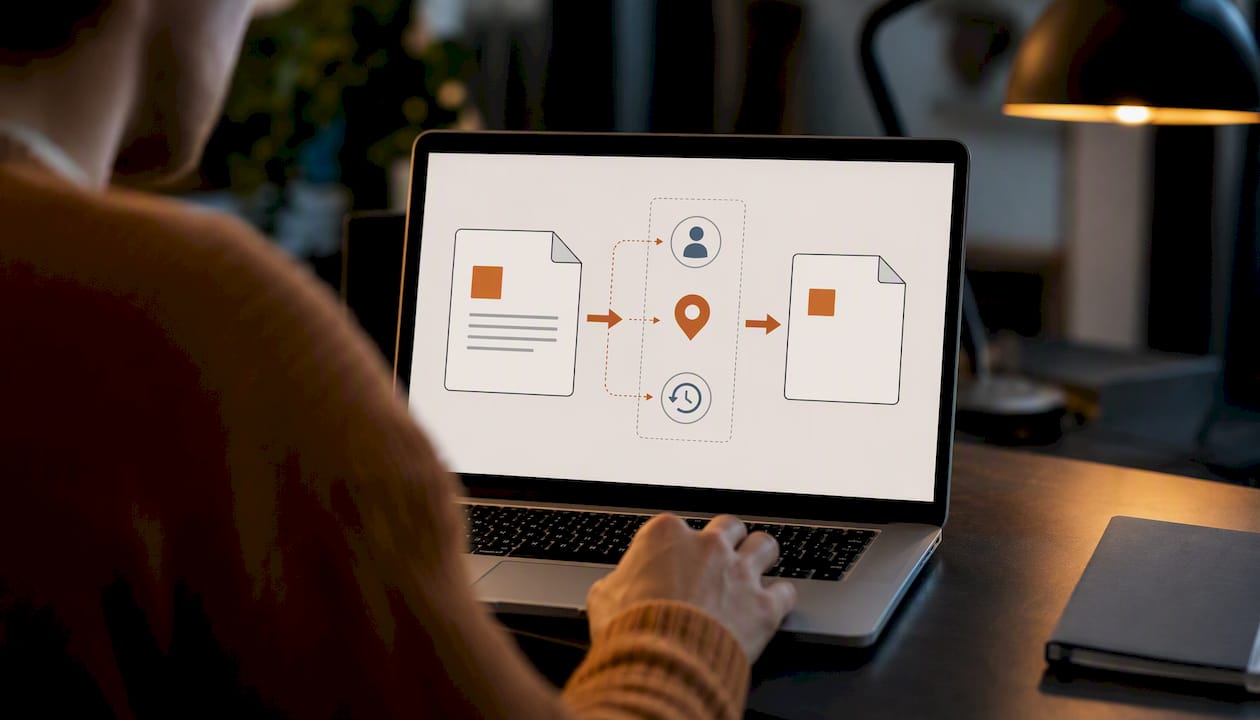
Avoid sending raw database exports or spreadsheets containing full personal records when a filtered or redacted version would do the job. If a recipient only needs three columns from a fifty-column spreadsheet, send the three columns.
For images and scanned documents, convert to PDF rather than sending loose image files when the content includes signatures, ID numbers, or financial details. A PDF combiner consolidates multi-page scans into a single file, which is easier to encrypt and track than a folder of individual images.
Encryption Standards: What's Actually Protecting Your File
Not all "encrypted" transfer tools mean the same thing, and the difference matters more than most people realize.
Transit encryption, usually TLS, protects your file while it's moving between your device and the server. Nearly every reputable service has this. It's the baseline, not the differentiator.
At-rest encryption protects the file while it sits on the provider's servers. WeTransfer documents this approach, encrypting files during upload and while stored, alongside optional password protection and expiration settings for paid accounts. This stops someone who breaches the server's storage from reading raw files.
End-to-end or client-side encryption goes further: the file gets encrypted on your device before it ever leaves, and only the recipient's device can decrypt it. The provider never holds a readable copy at any point. Platforms built around this model, including dedicated end-to-end encryption services, often use split-key architectures where no single party, including the vendor, holds the complete decryption key alone.
For most personal transfers, at-rest encryption from a reputable provider is sufficient. For legal, medical, or financial data, insist on client-side encryption specifically, and confirm the provider can't decrypt your files even if legally compelled to try.
An Operational Checklist for Teams That Move Large Files Often
The workflow that holds up under repetition is simple: prepare the file and hash it, encrypt before upload, transfer through a method matched to sensitivity, verify the checksum on arrival, then log the exchange somewhere searchable. Escalate to managed transfer or physical shipment once volume or compliance needs outgrow ad hoc links. Skipping steps under deadline pressure is where most leaks actually start.
— Andreas
Send Files Securely Without Building Infrastructure
Setting up SFTP or a managed transfer platform makes sense for high-volume compliance work, but it's overkill if you're sending a handful of large files a week and don't want to manage servers or credentials. Pingfloat's File Sharing & Secure File Transfer tool gives you browser-based sharing with password protection and configurable security settings, without the setup overhead SFTP requires.

It maps directly onto the decision checklist above: pick your security settings, generate a link, send it, and verify the download. No account is required to start, so you can test it on a real file today. If you're moving large files regularly enough to need higher limits, saved history, or team access, an upgrade can cover those needs without switching tools. Try the file transfer tool on your next large send, and check your endpoint's HTTPS setup with Pingfloat's SSL checker while you're at it.